Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on CyberSecurity for Applications, Services and Infrastructure, and related technologies.

Redact PII at the edge - and still be able to search for it

Ask a platform team why their application logs aren't in their observability backend and you'll often get a one-sentence answer: And, that's where the conversation ends. The logs stay in a silo. Or, they don't get collected at all. The team loses the troubleshooting signal, and nobody revisits the decision because the alternative looks like a compliance violation. Application logs in healthcare, aviation, insurance, and retail are full of personal information that should not be stored in plain text.

Run More Internal Hackathons

Internal hackathons are a powerful way to let your teams explore ideas and work together on something fun besides the same old stuff for work. Maybe they want to build something brand new, maybe they want to knock out things that are on the backlog that never get prioritized, or maybe they want to work on something fun but completely unrelated to work.

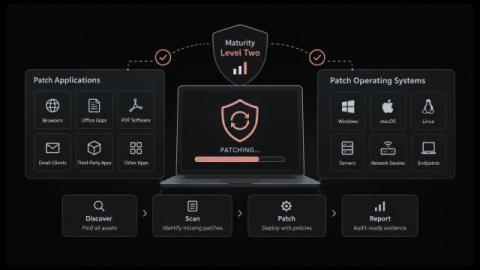
The Essential Eight: Patching Applications and Operating Systems at Maturity Level Two

Why do so many patching programs pass every internal check and still come back from an Essential Eight assessment rated at Maturity Level One? The answer is rarely speed. Teams that miss the mark are usually patching their servers, browsers, and office suites on schedule, then losing the rating on the fifty applications nobody put on a list. Maturity Level Two is where the Essential Eight stops asking how fast you patch and starts asking how much you can see.

SBOMs are easy for one project, monumental at scale

Think of an SBOM as your ingredient list. A common language describing everything that goes into a piece of software, every dependency and version, in one place. This video covers why SBOMs have gone from niche to mandatory, and why they're harder to pull off than the concept suggests: The concept is simple. Operationalizing it across a large, diverse tech stack is where it gets hard.

AI Agents on Kubernetes 101: From Laptop Script to Production Pod

In short, this is a beginner’s guide to deploying an AI agent on Kubernetes. You will containerize an agent, store its API key as a Kubernetes secret, write a deployment with health probes and resource limits, expose it with a service, and lock down its network egress, in that order, with a working manifest at every step. On a local kind cluster the whole walkthrough takes about an hour.

PCI DSS Requirement 10: Logging and Monitoring in v4.0.1

Version 4.0 renumbered PCI DSS Requirement 10 from end to end, and the Council retired v3.2.1 on 31 March 2024. Sub-requirement numbers written before then mostly point somewhere else now. Four more Requirement 10 rules changed status on 31 March 2025, automated log review among them. Checking your numbering against v4.0.1 costs an afternoon and saves a finding. In this blog, you will: PCI DSS Requirement 10 covers audit logging and monitoring across the cardholder data environment.

Why Most Security Firms Miss Their Incident Prevention Window

Security operations managers face a critical paradox: their teams are designed to respond to incidents, but the incidents that matter most are the ones that never happen. The difference between a security firm that prevents problems and one that merely responds to them comes down to a single, often-overlooked factor: whether they can see what their guards are actually doing in real time. When operators lack live visibility into patrol locations, guard status, and emerging threats, they're always one step behind.