Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on CyberSecurity for Applications, Services and Infrastructure, and related technologies.

How long does it take to replace every certificate after a CA distrust?

Last week we moved every certificate in one of our products to a new CA in 10 minutes. It was six certificates and 18 deployments. I said issuance was the part that slows down, because most CAs limit how fast you can order, and then I waved it off. A reader did the math for me. Some organizations run 30,000 certificates, they claimed, and that’s common at MSPs, telcos, and government agencies. Google Trust Services takes 100 orders an hour by default.
The Jolokia Problem: Eight CVEs, One Door in Apache ActiveMQ

The Apache ActiveMQ Jolokia endpoint has been the route to remote code execution in three separate years. In 2023, it was reflection into the JVM. In 2024, a default configuration left it without a login. In 2026, it was the broker's own management operations, patched in March, exploited in April, and reopened three more times by summer.

What a 'Kill Switch' Actually Means for Your Agent Fleet

In short, in the five weeks to 27th October 2026, Okta, Satya Nadella, the Cloud Security Alliance and Salesforce each put the words “kill switch” or “emergency brake” next to AI agents, and the AI Kill Switch Act, introduced in the US House on 23rd July, would require the largest model providers to be able to throttle, suspend or shut their systems down on order. Every one of those switches stops something, and none of them stops the same thing.

The $6.3B Binance Hack: What Happened and What It Teaches Security Teams About Investigation

TL;DR On October 29, 2026, attackers drained about $6.3 billion in crypto assets from Binance’s hot wallets, the largest crypto theft on record. Binance says the incident may have started with a compromised laptop, but its investigation has since found additional points of breach, and the root cause is still being confirmed. For engineering and security teams, the lesson is about how quickly you can reconstruct what happened across many systems once something goes wrong. In this post.

The Secure PaaS Alternative: Keep the PaaS Experience, Run It on Your Own Cloud

Railway, Northflank and seven other developer platforms disclosed breaches in October 2026. Here is why a shared PaaS turns one breach into everyone's breach, how Qovery gives you git-push deploys while your apps and data run in your own AWS, GCP, Azure or Scaleway account, and what Qovery still holds. Romaric founded Qovery to make Kubernetes accessible to every engineering team. He writes about platform strategy, developer experience, and the future of cloud infrastructure.

It's a Critical CVE, Now What?

Bryan Peace Leon Adato break down what exactly security-minded IT folks - whether they work in SRE, dev, networking, or more esoteric disciplines - should do when a new, critical, apocalyptic vulnerability is announced. They walk you step by step through research, analysis, and how to protect your company if a patch isn't out yet. Along the way they muse about the nature of the industry, the sudden spike in CVEs, and where to find the best hard cidr to take the edge off.

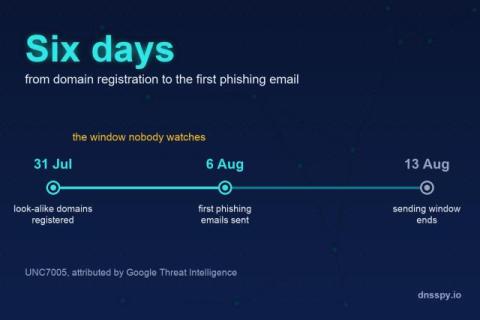
Six Days: What UNC7005 Shows About the Gap Between Domain Registration and Attack

On 20 August, Google Threat Intelligence published an analysis of a phishing cluster it tracks as UNC7005. Google assesses with moderate confidence that the cluster is connected to ICE RELIC, the Russian actor formerly tracked as APT29 and also known as Midnight Blizzard.

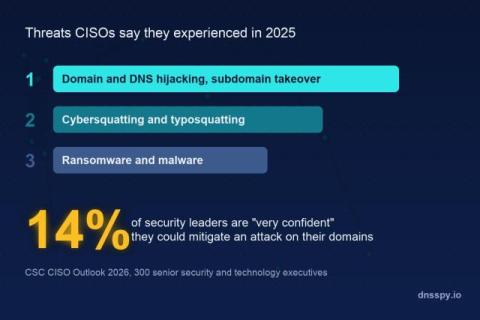
CISOs Now Rank Domain and DNS Hijacking Above Ransomware

CSC's CISO Outlook 2026 report surveyed 300 senior technology and cybersecurity executives in the first quarter of 2026, split evenly across North America, Europe and the UK, and Asia-Pacific. When asked which cyber threats they had actually experienced in 2025, not which ones worried them but which ones happened, the answer at the top of the list was domain and DNS hijacking, and subdomain takeover. Ahead of ransomware. Ahead of malware.

How Does a Domain Protect Critical IT Infrastructures?

A digital address routes traffic and anchors trust. The domain is far more than a convenient label that users type into a browser, since it carries out essential functions that keep critical systems connected, authenticated, and protected from harm. For organisations running mission-critical operations, it functions as a gatekeeper that determines whether legitimate users reach a service and whether attackers are turned away at the door.