Operations | Monitoring | ITSM | DevOps | Cloud

The Truth About End-to-End Testing Explained #softwaretesting #endtoendtesting #devops #qualitytest

End-to-end (E2E) testing brings your entire system together in a staging or UAT environment to test real user paths and ensure core functions work as expected. However, because E2E tests are non-comprehensive and miss edge cases, they must be combined with other testing methodologies. Learn more: speedscale.com.
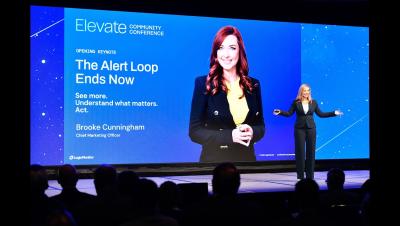
LogicMonitor Elevate 2026 Keynote: Trusting AI to Act

LogicMonitor Elevate 2026 keynote: what it takes to trust AI to act in IT operations. Built for IT ops leaders, SREs, and MSPs. The Chicago opening keynote covers moving beyond the alert loop, where people have acted as the integration layer between tools. IT teams are automating incident response by giving AI context, clear guardrails, and governance, with people accountable and in control. @globalfoundries CIO Vishal Mehra shares how his team's doing it.

Good Agents Need Good Managers: What We Heard at Innovation Week

I used to joke that I got my best parenting ideas from management books, and my best management ideas from parenting books. Now, I'm extending it to agents. Hear me out. When you're teaching a teen how to drive, you don't hand them the car keys on day one. You start in an empty parking lot. You ride along and ask them to talk through what they're doing.

Nokogiri 1.19.5 Closes Three Security Advisories and a Wave of Compaction Crashes

Nokogiri sits under so much Ruby code that its patch releases are worth reading even when the version number looks routine. 1.19.5 is a patch release carrying three security advisories and a long list of crash and memory fixes, so it’s worth pulling in on your next dependency pass.

CVE-2026-109518 APT vulnerability fixes available

Max Justicz discovered and responsibly disclosed a vulnerability in APT, the package manager used in Debian, Ubuntu, and derivative Linux distributions. The vulnerability has been assigned the identifier CVE-2026-109518 and has a severity of High. An on-path attacker who can manipulate the HTTP traffic between a system and an archive server can trigger the installation of an attacker-controlled.deb package file and obtain root privileges on the target system.

10 Best Paging Software Solutions for Healthcare and IT Teams in 2027

When a critical incident occurs, reaching the right person quickly can make all the difference. Whether it’s a hospital contacting an on-call physician or an IT team responding to a server outage, reliable paging software helps ensure urgent messages reach the people responsible for taking action. Traditional pagers have long been used in hospitals, emergency services, and other mission-critical environments.

How dedicated database monitoring protects customer experience and reduces operational risk

Many outages, slowdowns and failed transactions start in the database, often well before anyone outside the data team knows something’s wrong. By the time they do, customers are already affected: payments fail, services stall and people can’t do what they came to do. The organisations that keep this risk under control close three gaps. They stop problems before they disrupt customers and the services they depend on. They find the cause in minutes, and fix it quickly.

Running Production with Agents w/ Rootly AI, NVIDIA, Replit, PostHog, & WorkOS

AI agents are writing code, investigating incidents, and changing how infrastructure teams work. For SREs, that brings new questions about reliability: when to trust an agent, how to catch its mistakes, and who owns the outcome. ​The panel ​Tim Glaser - Co-founder and CEO at PostHog​Michael Grinich - CEO and Founder at WorkOS​Vishakha Sadhwani - Sr. Solutions Architect at NVIDIA​Niall O’Higgins - Engineering Lead at Replit​Sylvain Kalache (Moderator) - Head of AI Labs at Rootly AI.