Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on CyberSecurity for Applications, Services and Infrastructure, and related technologies.

The Swedbank Outage shows that Change Controls don't work

This week I’ve been reading through the recent judgment from the Swedish FSA on the Swedbank outage. If you’re unfamiliar with this story, Swedbank had a major outage in April 2022 that was caused by an unapproved change to their IT systems. It temporarily left nearly a million customers with incorrect balances, many of whom were unable to meet payments.
Sponsored Post

Agent and agentless: An ongoing battle

Observability of an SAP environment is critical. Whether you have a large complex and hybrid environment or a small set of simply architected systems, the importance of these systems is probably crucial to your business. Just thinking about system outages keeps us up at night, let alone the pressure of system performance, cross system communication and proper backend processing.

How to Conduct a Workplace Risk Assessment

Workplaces are unavoidably hazardous places, no matter how anodyne they may seem from outside. Administrative offices may have chemical cleaning products lurking behind kitchenette cupboards, or electrical hazards within arm's reach of a desk. For this reason, risk assessments are a vital part of every business' health and safety programmes. How should one be conducted, though?

How to secure your MLOps tooling?

Generative AI projects like ChatGPT have motivated enterprises to rethink their AI strategy and make it a priority. In a report published by PwC, 72% of respondents said they were confident in the ROI of artificial intelligence. More than half of respondents also state that their AI projects are compliant with applicable regulations (57%) and protect systems from cyber attacks, threats or manipulations (55%). Production-grade AI initiatives are not an easy task.

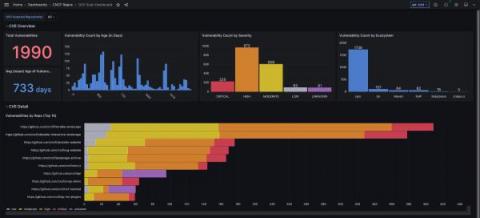
How to manage CVE security vulnerabilities with Grafana, MergeStat, and OSV-Scanner

Patrick DeVivo is a software engineer and founder of MergeStat, an open source project that makes it possible to query the contents, history, and metadata of source code with SQL. The security posture of software supply chains has been a significant topic lately. Recent high-profile breaches have shown the importance of managing risks from third party code. Take, for example, the Log4Shell vulnerability (tracked as CVE-2021-44228 — Grafana Labs was not affected).

Revisit - the Balancing Act of Staying Secure While Working From Home: Ep. 11

Welcome to Security Insights: where best-practice cybersecurity meets the real-world risks, workplaces, and roadblocks you face every day. Join Chris Goettl, head of Endpoint Security Product Management, and Ashley Stryker, your cybersecurity "rubber duck", as they review the security strategies and tactics that truly matter to the information security teams protecting organizations, agencies, and businesses like yours.

Achieving High Availability (HA) Redis Kubernetes clusters with Calico Clustermesh in Microsoft AKS

According to the recent Datadog report on real world container usage, Redis is among the top 5 technologies used in containerized workloads running on Kubernetes. Redis database is deployed across multi-region clusters to be Highly Available(HA) to a microservices application.

The Ripple Effect of Meta's $1.3 Billion GDPR Fine for Businesses That Handle Data

Meta, the parent company of Facebook, has been fined a record €1.2 billion ($1.3 billion) by the European Union for violating its data privacy laws. The fine was issued by Ireland’s Data Protection Commission, which is Meta’s lead regulator in the EU, and is the largest ever levied under the EU’s General Data Protection Regulation (GDPR), which went into effect in 2018.