Operations | Monitoring | ITSM | DevOps | Cloud

Microsoft Has a Bigger Problem Than Anyone Realizes

Microsoft just released over 1,400 security patches, including three zero-day vulnerabilities, one of which is already being exploited. But is this a sign of better security or a much bigger problem? In this ShipTalk discussion, we break down Microsoft's massive Patch Tuesday release, the challenges of managing thousands of vulnerabilities across enterprise environments, and whether AI is helping Microsoft find problems too late in the software development process.

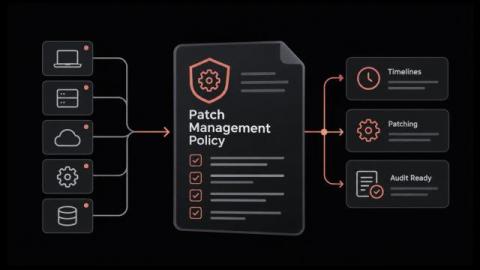
What a Patch Management Policy Should Contain to Keep Systems Secure and Audit-Ready

Who decides how fast a critical patch goes out, and who signs off when a production server can't be restarted? For many IT groups, the answer is a mix of one senior admin's judgment, an old ticket and a shared spreadsheet. It holds up fine right until an auditor asks for proof, or that admin leaves. A written policy replaces that guesswork with rules people have agreed to. Owners are named, deadlines are fixed, and there's a plan for the system that can't be patched on time.

SAP Security Patch and Vulnerability Monitoring Guide

Avantra monitors SAP security patch status across entire landscapes, checking each newly published SAP HotNews note against every managed system and tracking which systems still need it. It covers the patch side of SAP vulnerability management, which is a different job from code-level vulnerability scanning.

Autonomous Patch Management | Ivanti

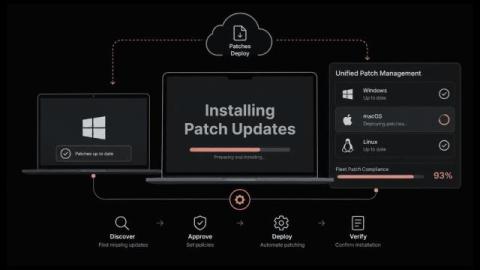
New vulnerabilities emerge every day and thousands of endpoints change constantly — it's a continuous race against time. Patching isn't just deployment; it's manual handoffs and incomplete visibility that leave organizations exposed. This video shows how Ivanti Neurons for Patch Management provides immediate, authoritative insights into your IT estate so you can close security gaps faster.

5 Signs Your In-House Ops Team Has Hit Its Ceiling (And What to Do Next)

Every small ops team reaches a point where the work outgrows the people. Tickets arrive faster than they close, the pager goes off at 2 a.m. for the third time this week, and the roadmap quietly slips another quarter. Leadership sees missed deadlines. The team sees a system with no slack left in it. The hard part is spotting the ceiling before it turns into attrition or an outage. This article covers five warning signs that a team is stretched too thin, then shows how to decide what to keep in-house and what to hand off.

It takes a hacker 48 hours to exploit a vulnerability. Why does it take 43 days to patch it?

It is not always possible to patch vulnerabilities as quickly as hackers exploit them, but recent figures show just how much this gap has widened. FortiGuard Labs estimates that the time between the disclosure of a critical vulnerability and its active exploitation has dropped sharply to between 24 and 48 hours. By contrast, Verizon’s 2026 Data Breach Investigations Report shows that organizations take a median of 43 days to complete vulnerability remediation.

macOS Patch Management for Mixed Windows and Mac Fleets

How many Macs in your environment are running an OS build that your patch compliance report has never counted? In most mixed Windows and Mac deployments, the Windows side is managed by policy and the Mac side is managed by hope. Designers, executives, and engineering leads install updates when a notification interrupts them, and otherwise dismiss the prompt for months.

Your patch window just went from 30 days to hours

Thanks to AI, vulnerability disclosures are exploding. In mid 2026, we're seeing 130+ a day and climbing, with roughly a quarter already being exploited in the wild before they're even disclosed. The result: security teams that used to have 30 days to respond now feel pressure to issue patches in a few days or hours. This video covers why "are we safe?" isn't a question you get to answer once: That last drill is what separates teams that panic when a real incident hits from teams that already know the answer.

How Smarter Patch Management Strengthens IT Operational Resilience

Operational resilience depends on an organization's ability to maintain essential systems when disruptions occur. Cyberattacks, software failures, and configuration problems can all threaten that stability. Yet one of the most preventable sources of risk is also one of the most persistent: outdated software. Patch management is often treated as routine maintenance. In practice, it supports both cybersecurity and service continuity. A well-structured patching process reduces exposure to known vulnerabilities while helping IT teams keep applications and operating systems reliable.