Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on CyberSecurity for Applications, Services and Infrastructure, and related technologies.

Agentic SOC Tools 2026 Buyer's Guide

As we write this in Q4 2026, the agentic SOC solution market consists of a very complex array of products. Solutions being sold as "agentic SOC" include standalone AI SOC analysts, agentic SOAR platforms, AI agents embedded in SIEM/XDR products, and managed SOC services using autonomous agents. This makes the buying landscape complex, to say the least. This guide covers the key factors to consider when evaluating agentic SOC tools and provides a concise overview of the leading solutions to help you narrow down your shortlist.
Business Process Outsourcing: A Practical Guide to Choosing What to Keep In-House

Business process outsourcing, commonly called BPO, involves using a third party to perform selected business activities. A useful starting point is understanding what BPO means in practice: the business delegates specific processes while remaining responsible for its priorities, customer promises, and final results.

Strengthening the Security of Qovery's Access to Your AWS Account

Qovery now sends your organization ID as the sts:ExternalId when it assumes the IAM role in your AWS account, and the role's trust policy only accepts it on behalf of your organization. Your role is already updated. If you manage it with the qovery-role-creation CloudFormation stack, update the stack to the latest template. Romain is a staff engineer at Qovery working on the control plane and AI integrations. He writes about distributed systems, incident response, and MCP-based tooling.

Introducing Ergo: explainable policies on OPA

When an auditor tests a control, they ask two questions about each change: was the control met, and what evidence shows how that result was reached? Most automated controls can answer the first. A Rego policy returns allow: true or allow: false, but says nothing about what it checked. Engineers can hand-write violation messages to explain a failure, but a passing check leaves no record at all. When an auditor asks how a change passed, someone has to reconstruct the answer.

How to Secure Your PHP Infrastructure and Remediate PHP2Shell with Puppet

The detailed flaw coined “php2shell” is inherent in the PHP language itself, with multiple versions of PHP affected that have been released on the last decade. Ryan Austin, a Calif researcher who helped uncover the issue told the BBC it was, “The most serious vulnerability I’ve ever found". Wiz wrote in a blog post about the detailed findings that would allow hackers to exploit the PHP2Shell issue and take control of an affected web server.

How to Patch PHP2Shell Across Every Server and Prove Each Fix to Auditors

When a critical flaw surfaces in the language behind a large share of your web applications, how quickly can your organization name every server that runs it? PHP2Shell puts that question in front of every IT leader who runs PHP. The answer decides how long the business stays exposed. Here's the short version. PHP2Shell covers two flaws in the PHP engine, and either one lets an attacker run code on a web server with no login at all.

How Upsun handled PHP2Shell: protection in place 22 hours before the patch

On 21 October 2026, the team behind PHP released an emergency fix for two critical security flaws. PHP is the programming language behind a large share of the web, including WordPress, Drupal and many online stores. Researchers at Wiz named the flaws PHP2Shell. An attacker could use them to take control of a website without ever logging in. Updating a website, its CMS, or its plugins doesn't help. The only real fix is (and was) a new version of PHP itself.

Security Just Hit Machine Speed

What if we could eliminate vulnerabilities before they become a problem? Neil Watkins from Burns & McDonnell explains how AI, automated security assessments, and Harness CI/CD capabilities could transform vulnerability management. From reducing attack surfaces to rapidly responding to critical zero-day vulnerabilities, the future of security is about moving faster without slowing down developers.

How to Stop Secrets Leaking From Your Deployment Platform, and How Qovery Stores Yours

Railway's disclosure of leaked customer environment variables is a reminder that deployment platforms hold the keys to everything. Here is how secrets leak from platforms, the practices that prevent it or limit the damage, and exactly how Qovery stores secrets across its control plane and your data plane, with AWS Secrets Manager, Parameter Store, GCP Secret Manager, Doppler and Infisical. Romaric founded Qovery to make Kubernetes accessible to every engineering team.

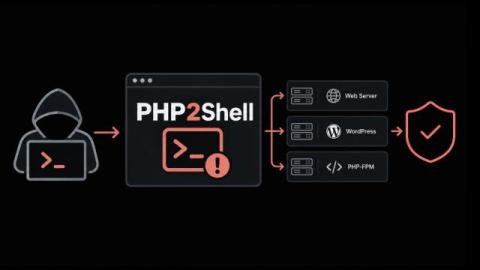
PHP2Shell: What the Critical PHP Vulnerabilities Mean for Your Servers

TL;DR On October 21, 2026, PHP released emergency patches for two critical flaws known together as PHP2Shell (CVE-2026-109618 and CVE-2026-109619). An attacker with no credentials can use them to run code on a PHP web server, in some cases with a single HTTP request. Upgrade to PHP 8.2.35, 8.3.36, 8.4.27 or 8.5.12 now. Then go through your logs, because exploitation attempts were recorded before the patch shipped. In this post.