Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on DevOps, CI/CD, Automation and related technologies.

How to Establish a Culture of Secure DevOps

We’re constantly told to “Shift Left” and that Secure DevOps is the only way to have confidence in your cloud native applications. But speaking to end-users and industry colleagues, it’s clear that there are some major challenges in adopting Secure DevOps. If we read our history books, we know that DevOps wasn’t successfully adopted by buying tools, and a true cultural movement towards DevOps wasn’t established by having a small dedicated team of DevOps specialists.
Engineering solutions to security issues

Software engineering teams have always looked for ways to increase code creation efficiency, reduce code vulnerabilities, and improve security processes. Many are now shifting security left, establishing security controls and testing — specifically integration testing — at an earlier phase in the software development lifecycle (SDLC).

Packet Capture Without "tcpdump" for Go Apps in Kubernetes

Every developer knows there are some utilities that are completely indispensable from their workflows. The programmer’s toolbelt, if you will. These toolbelts are usually different from person to person, but if there is one tool that everyone should use or at least know how to use, it is tcpdump. If you are unfamiliar, tcpdump is a tool that allows you to dump and inspect live network traffic being observed on a network interface.

Visualize live dependencies with the Request Flow Map

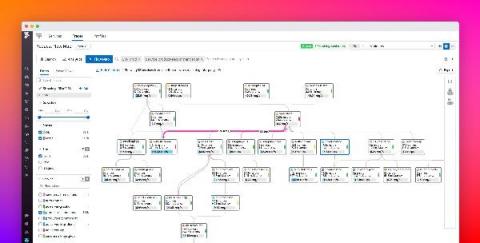
Modern applications are often composed of countless distributed services, which makes it difficult to understand dependencies, isolate bottlenecks, and remediate errors. Datadog APM helps you tackle this complexity by allowing you to search and analyze 100 percent of your traces in real time. But without a dynamic view of your architecture, it can still be challenging to contextualize a specific request without getting lost in the details.

Resilience, DevSecOps, and other key takeaways from RSAC 2021

For the first time in its 30-year history, the 2021 RSA Conference was a virtual-only event, and not in its usual time during the spring. But, with 20,000 registrants joining for the various sessions, it was a testament to this year’s conference theme of resilience.

Pragmatic Incident Response: 3 Lessons Learned from Failures

In my past experience as an SRE I’ve learned some valuable lessons about how to respond and learn from incidents. Declare and run retros for the small incidents. It's less stressful, and action items become much more actionable. Decrease the time it takes to analyze an incident. You'll remember more, and will learn more from the incident. Alert on pain felt by people — not computers. The only reason we declare incidents at all is because of the people on the other side of them.

A Comprehensive Cloud Migration Checklist

More and more cloud providers are emerging and spreading their business across different regions in the current times. As a result, customers want to reduce their IT workload and migrate their product or application to a cloud-based environment. The primary reason behind this is that the cloud heavily reduces the overheads of investing in IT infrastructure, hardware upgrades, maintenance, etc.

How Traffic Engineering Can Lead to a Smooth Transition to 5G

Communications Service Providers around the world have experienced an unprecedented explosion in demand for bandwidth due to several driving forces including more video streaming, the growing popularity in areas like cloud gaming and the increasing move to the cloud to name a few.