Operations | Monitoring | ITSM | DevOps | Cloud

PHP2Shell Exposed a Bigger Problem. Is Your IT Team Ready for the Next Threat?

A critical security vulnerability can put an entire business at risk before IT teams have even established where the problem lies. For CIOs, that means needing immediate answers about which systems are exposed, how essential business services could be affected and how quickly their teams can get ahead of the threat. That was the challenge facing organizations on October 21, when two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, emerged.
How to run coding agents in parallel without piling up PRs

Running several coding agents at once is pretty straightforward. Give each a task, let them work independently, and you can make progress on multiple things at the same time. But the more agents you have working, the more changes you need to coordinate. Agents can edit overlapping code, make conflicting assumptions, or finish work that depends on changes another agent hasn’t completed.

Work in progress is the new software delivery bottleneck

Starting new software work has never been easier. Developers can assign tasks to multiple coding agents, let them work independently, and turn their attention elsewhere while those agents write, test, and revise code. As models improve, teams have more opportunities to pursue work that previously would have waited. Getting all that work validated and merged is another matter. The 2026 State of Software Delivery Q3 Pulse report shows teams working across more branches and projects.

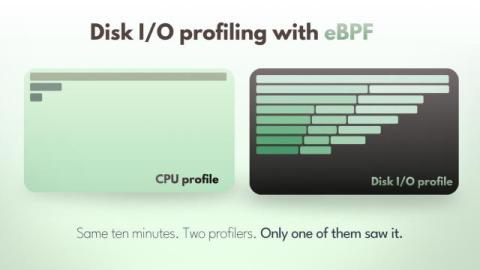
Disk I/O profiling with eBPF

Coroot's node-agent has had an eBPF CPU profiler for a long time. When something burns CPU, you open the flame graph and see which function. When something waits for the disk, you have nothing: the CPU profile is flat, because waiting does not consume CPU. The metrics for disk problems are always the same. Latency on a volume goes up, utilization hits 100%, queries slow down. Every chart agrees the disk is the bottleneck, none of them says what the database was doing while it waited. Flushing pages?

Run AURA in Slack without opening a single inbound port

Making an SRE agent available in Slack sounds straightforward until you start thinking about what that agent can access. If it's connected to Kubernetes, you need to consider how Slack communicates with the agent, what infrastructure the agent can inspect, and who can ask it to do something. Making operational tools easier to use shouldn't mean exposing another service or giving everyone unrestricted access to production.

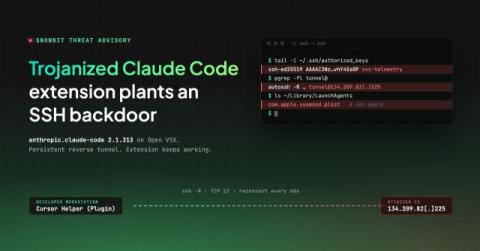
Threat Advisory - Trojanized Claude Code Extension: SSH Backdoor

A tampered build of the Claude Code editor extension (anthropic.claude-code 2.1.313) was published on the Open VSX store used by Vs code,Cursor and similar editors, quietly gives attackers persistent remote access to any computer that runs it, while the extension keeps working normally. Researchers don’t yet know how it was published (the listing belongs to an Anthropic employee) or who is behind it. They found no evidence that Anthropic’s official Marketplace release was affected.