Operations | Monitoring | ITSM | DevOps | Cloud

Match monitoring depth to workload needs with Infrastructure Basic

A back-office server that runs out of disk space can interrupt an important internal workflow. A process that stops on a staging host can delay development. Although workloads like these might not require application-level instrumentation, teams still need to know when the hosts that support them require attention. Without a monitoring solution tailored to these requirements, teams have to apply more monitoring than the workload needs, maintain a separate tool, or accept a gap in visibility.
Meet the new Explore: every question, one place

From the first alert to the root cause, without leaving the page. TL;DR: Investigating an incident is a series of quick questions, each one leading to the next. Until now, Explore made you stop between questions to translate them into syntax, switch modes or rebuild a chart. The new Explore lets you go straight from one question to the next: one workspace, any dataset, any team, any way you like to ask. Here’s what that looks like on a real night on call.

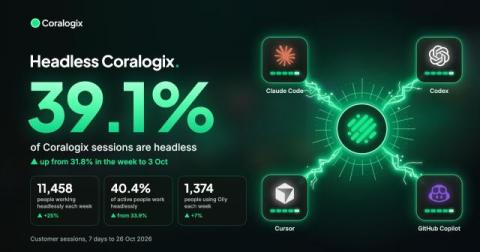
39% of Coralogix sessions are now headless

We set out to understand how customers were using Coralogix from outside the web app. Olly answers questions about a system in plain language. Coding agents query logs, examine traces, read metrics and configure the platform through the Coralogix CLI and MCP server. We wanted to see how much of this was becoming part of everyday work. In the week of 20–26 October, 39% of Coralogix sessions included Olly, the CLI or MCP.

The Deconstructed Database at Datadog

As Datadog scaled to handle over a hundred trillion daily events, our engineering teams built their own custom query engines to keep things fast. While this helped teams move quickly, it also created silos that made it tough to analyze data across different products. To keep growing and support AI, we had to find a way to bring these engines together using open standards without slowing anyone down or risking reliability.

Measuring What Matters in AI Applications

AI has become incredibly sophisticated and changed the way we build and power applications. But it has also introduced volatile complexity that challenges how we ensure reliability and protect user experiences. Join our panel of experts as they discuss the realities of building AI-powered applications. They’ll talk about how testing has evolved, share insights into how they do evals and experiments, and offer advice on how to get better visibility into how your AI is performing.

Why AI-Generated code still needs tests

AI has made life easier for us developers. Dozens of AI tools are getting more advanced every day, shortening and speeding up the development cycle. Converting an idea into a concrete MVP is faster than ever before. Intelligent models turn your ideas into a working project with just a few prompts. End users or product owners can see the application, use the beta version, and give feedback on the spot.

Demystifying NODE

Having spent significant time working with the Network Observability Deployment Engine (NODE), I can confidently say that modernizing network observability does not have to feel like black magic. NODE simplifies how we deploy, scale, and manage complex network observability environments. Whether you're working with Kubernetes for the first time or streamlining an enterprise monitoring stack, NODE brings structure and clarity to the setup process. At its core, NODE relies on two main building blocks.

How AI Is Changing Cybersecurity and Exposing Decades of Bad Code

Was this the worst week in cybersecurity? AI-discovered PHP2Shell vulnerabilities, the LiteLLM supply chain attack, and reports of unauthorized AI agents accessing bank accounts are exposing serious weaknesses in software security. But is this really a cybersecurity problem, or has AI exposed decades of poor software engineering decisions? In this episode of ShipTalk, Martin Reynolds and Adam Arellano break down a remarkable week in AI security and debate whether engineering or security teams should be responsible for fixing what comes next.