Operations | Monitoring | ITSM | DevOps | Cloud

Detecting the Sudo Baron Samedit Vulnerability and Attack

On January 26th, 2021, Qualys reported that many versions of SUDO (1.8.2 to 1.8.31p2 and 1.9.0 to 1.9.5p1) are vulnerable (CVE-2021-3156) to a buffer overflow attack dubbed Baron Samedit that can result in privilege escalations. Qualys was able to use this vulnerability to gain root on at least Ubuntu 20.04 (Sudo 1.8.31), Debian 10 (Sudo 1.8.27), and Fedora 33 (Sudo 1.9.2), some of the most modern and widely used Linux operating systems.

Detect CVE-2020-8554 using Falco

CVE-2020-8554 is a vulnerability that particularly affects multi-tenant Kubernetes clusters. If a potential attacker can create or edit services and pods, then they may be able to intercept traffic from other pods or nodes in the cluster. An attacker that is able to create a ClusterIP service and set the spec.externalIPs field can intercept traffic to that IP. In addition, an attacker that can patch the status of a LoadBalancer service can set the status.loadBalancer.ingress.ip to similar effect.

New Vulnerability Exposes Kubernetes to Man-in-the-Middle Attacks: How to Mitigate CVE-2020-8554

A few weeks ago a solution engineer discovered a critical flaw in Kubernetes architecture and design, and announced that a “security issue was discovered with Kubernetes affecting multi-tenant clusters. If a potential attacker can already create or edit services and pods, then they may be able to intercept traffic from other pods (or nodes) in the cluster.” If a hostile user can create a ClusterIP service and set the spec.externalIP field, they can intercept traffic to that IP.

Mitigating Kubernetes Security Vulnerability when using ExternalIP Services (CVE-2020-8554)

Earlier this month the Kubernetes project discovered a security issue affecting multitenant clusters: If a potential attacker can already create or edit services and pods, then they may be able to intercept traffic from other pods (or nodes) in the cluster. An attacker that is able to create a ClusterIP service and set the spec.externalIPs field can intercept traffic to that IP.

SolarWinds Update on Security Vulnerability

On Saturday, December 12, our CEO was advised by an executive at FireEye of a security vulnerability in our Orion Software Platform which was the result of a very sophisticated cyberattack on SolarWinds. We soon discovered that we had been the victim of a malicious cyberattack that impacted our Orion Platform products as well as our internal systems.

Coordinated disclosure of XML round-trip vulnerabilities in Go's standard library

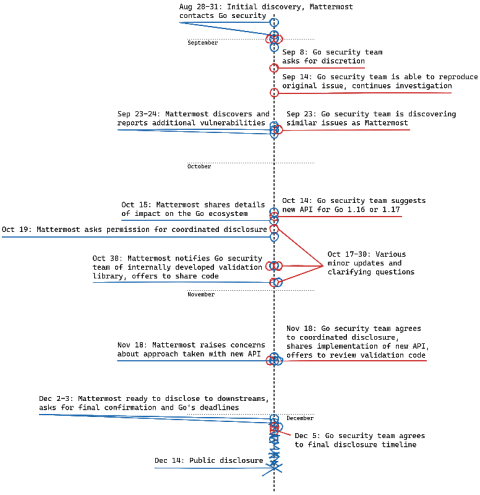
This blog post is a part of Mattermost’s public disclosure of three serious vulnerabilities in Go’s encoding/xml related to tokenization round-trips. The public disclosure comes as a result of several months of work, including collaborating with the Go security team since August 2020 and with affected downstream project maintainers since earlier this month.

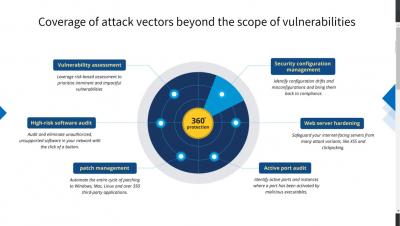
Vulnerability Management with ManageEngine Vulnerability Manager Plus

Vulnerability management is the cyclical process of identifying, evaluating, treating, and reporting on threats and vulnerabilities across your network endpoints. In this video, we take an in-depth look at the exhaustive threat and vulnerability management features of ManageEngine Vulnerability Manager Plus.

Ivanti Neurons for Patch Intelligence: Research, Prioritize, and Receive Improved Risk-Based Insights

Vulnerability remediation is still an ongoing struggle for organizations. A simple mistake could cause no issues, or it could set off a wide-scale, devastating, corporate breach. Why is this? There are many reasons. Security and Ops talk past one another. No one wants to be the one that broke something. Speed is hindered by ineffective testing.

Understanding and mitigating CVE-2020-8566: Ceph cluster admin credentials leaks in kube-controller-manager log

While auditing the Kubernetes source code, I recently discovered an issue (CVE-2020-8566) in Kubernetes that may cause sensitive data leakage. You would be affected by CVE-2020-8566 if you created a Kubernetes cluster using ceph cluster as storage class, with logging level set to four or above in kube-controller-manager. In that case, your ceph user credentials will be leaked in the cloud-controller-manager‘s log.