Operations | Monitoring | ITSM | DevOps | Cloud

What Is IT Change Management? Process, Types, and Best Practices

Last updated: Oct. 15, 2026 IT environments change constantly. The challenge is making those changes without creating unnecessary risk, outages, or delays. IT change management, called Change Enablement in ITIL 4, helps teams assess, authorize, implement, validate, and learn from changes that could affect an IT service. The goal is not to slow delivery. It is to improve change success while reducing disruption, recovery time, compliance risk, and impact on critical business services.

When five agents are looking at the same IT incident, which one makes the decisions?

It’s 2:14 am, and checkout latency at your largest retail store has tripled. Your observability platform’s agent has already posted to Slack that there is a connection pool exhaustion on the orders database, with a link to the trace. Your cloud provider’s agent reports a degraded network path in one availability zone. The AI SRE tool one of your product teams adopted last spring points to a deploy that went out at 1:50.

Is VPA "Good Enough"? How Kubex Delivers Enterprise-Ready Workload Optimization

Kubernetes workload rightsizing is one of those tasks everyone agrees is important and almost nobody enjoys doing by hand. Set requests too high and you pay for capacity that sits idle; set them too low and you invite CPU throttling, out-of-memory kills, and late-night pages. It’s no surprise, then, that many teams reach for the Vertical Pod Autoscaler (VPA) as their first step toward automated rightsizing.

Data Center Rack Density Just Crossed 11kW. Do You Have the Tools and Data to Keep Up?

Uptime Institute's Global Data Center Survey 2026 found that the average modal rack density exceeded 11 kW in 2026, up from 9 kW in 2025. “Modal rack density” means the rack density that is most common within a data center. Arguably, the more important trend is that rack densities are becoming more varied, with more facilities supporting a mix of conventional and high-density racks.

CVE-2026-74580: Possible VM Escape via the Vghost Vulnerability

CVE-2026-74580 is a high-severity Linux kernel bug in vhost, the subsystem that accelerates I/O for virtual machines. It gives a local user a reliable path to root on the host, and in some VM setups it lets a guest write into host memory. The CVE record has existed since August 21, 2026, but the full technical write-up, nicknamed "Vghost", only went public on October 12. It came with working exploit demos for both a local root escalation and a VM escape.

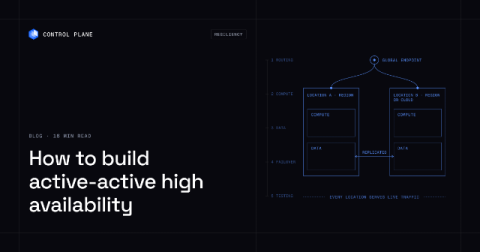
How to Build Active-Active High Availability Across Regions and Clouds

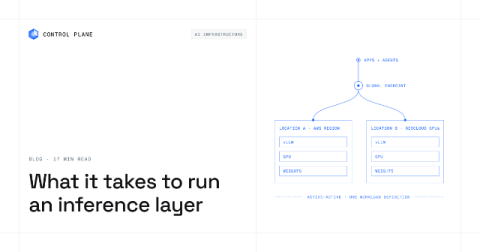
Active-active means two or more locations serve live traffic at the same time, with the application running in each and its data replicated across them, so no location sits idle waiting for a failover. You build it in five layers, and data is the hardest.

What Infrastructure Do You Need to Run an Inference Layer? A Production Guide

A production inference layer needs GPU compute sized to the model, a serving runtime such as vLLM or SGLang, orchestration that autoscales on queue depth, one endpoint with health-aware routing and failover, model weights cached near the GPUs, and observability, security, and cost controls.