The latest News and Information on Log Management, Log Analytics and related technologies.
In Cloud Logging, we understand that logging is a critical part of what it takes for you to operate reliable applications and infrastructure on Google Cloud. We’ve added new features to help you more easily store, find and control your logs. Today, we’re announcing a new default logging experience: Logs Explorer. Previously known as Logs Viewer Preview, Logs Explorer provides new tools for you to better understand and analyze your logs during the troubleshooting process.
Elastic Cloud on Kubernetes (ECK) is the official operator for provisioning Elastic Stack deployments in Kubernetes. It orchestrates not only day-one provisioning, but also has the processes and best practices for day-two management and maintenance baked in. If you want to run your own Elastic Stack deployment on Kubernetes, then look no further than ECK!
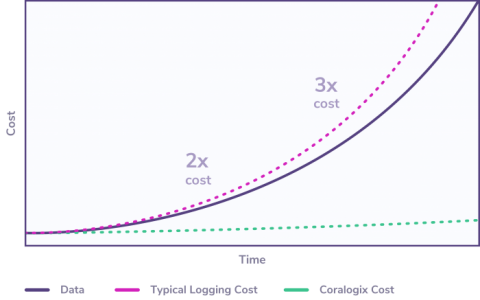
With the new Streama capability announced today, you no longer have to choose what to monitor and what to drop to manage your logging costs. For years, our customers have enjoyed the benefits of a log analytics platform that enables them to autonomously manage and analyze data in their cloud applications. Our machine learning engine empowers users to improve their system stability and accelerate their release cycles.
Logstash has a number of helpful plugins. We’ve covered the mutate plugin in great detail here, as well as Logstash grok, but it was time to go over some of the others. Here, the Logstash Prune Filter will get its due attention. Its existence owes to the need to remove fields according to select blacklists or whitelists of field names and their associated values. Put more curtly, it prunes the excess branches (fields) in your garden (your data).
Running an ELK stack provides unrivaled benefits for your organization, however, ELK issues will inevitably crop up. ELK is scalable, and largely agnostic of internal infrastructure, making it a great asset for SMEs and enterprises. However, successfully deploying and running an ELK stack is not without its difficulties. In order to keep your ELK stack running at optimum performance, you need to familiarize yourself with some of the most common ELK issues.
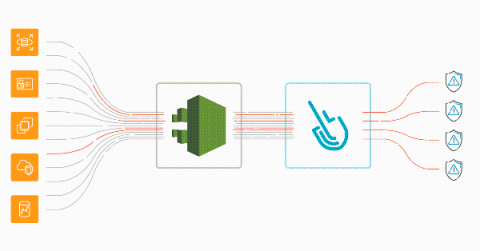
Implementing AWS threat detection with Sysdig Secure takes just a few minutes. Discover how to improve the security of your cloud infrastructure using AWS CloudTrail and Sysdig Cloud Connector. With the rise of microservices and DevOps practices, a new level of dangerous actors threatens the cloud environment that governs all of your infrastructure. A malicious or inattentive cloud API request could have a sizable impact on availability, performance, and last but not least, billing.
Effective log analysis can help you significantly reduce the time spent investigating and troubleshooting incidents. With the many different log analysis platforms available, it can be overwhelming to choose and difficult to know what to look for. In this short guide, we’ll share the top three things you should consider when selecting a log analysis platform for your business.
The main focus for cybersecurity teams — moving beyond compliance — is to deliver the level of security required to manage the likelihood of a breach and the potential impact to the business. This is more effective than simply focusing on the cost of delivering security services.