Operations | Monitoring | ITSM | DevOps | Cloud

Trusted SBOMs delivered with the JFrog Platform and Azure

SBOMs provide essential visibility into all the components that make up a piece of software and detail how it was put together. With an SBOM in hand it’s possible to determine if software contains existing security and compliance issues or is impacted by newly discovered vulnerabilities. The SBOM is imperative due to the White House’s cybersecurity executive order from May 2021 requiring them for all government software purchases and many private organizations following suit.

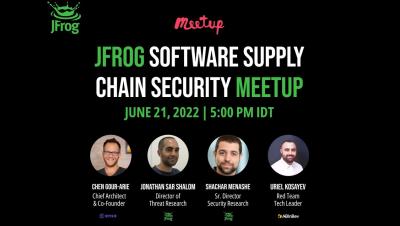
Supply Chain Security Meetup June 21 2022 (Sponsored by JFrog)

Software Supply Chain Security Virtual Meetup Open-source vulnerabilities are in many applications. While finding them is critical, even more, critical is remediating them as fast as possible. Securing your software supply chain is absolutely critical as attackers are getting more sophisticated in their ability to infect software at all stages of the development lifecycle, as seen with Log4j and Solarwinds.


JFrog Frogbot version 2

Frogbot scans every pull request created for security vulnerabilities with JFrog Xray and in version 2 it even opens pull requests for upgrading vulnerable dependencies to a version with a fix!. With Frogbot installed, you can make sure that new pull requests don’t add new security vulnerabilities to your code base alongside them. If they do, the creator of the pull request has the opportunity to change the code before it is merged.