Operations | Monitoring | ITSM | DevOps | Cloud

SIEM Pricing 2026: Major Providers Compared (& How to Lower Your Bill)

Every major security information and event management (SIEM) platform prices on the volume of data you send it. Microsoft Sentinel meters per gigabyte across two tiers. Splunk charges per gigabyte indexed or per compute unit. Google SecOps draws down a prepaid gigabyte credit balance. Elastic Security bills ingest plus retention, or the resources your cluster consumes. Three of the four keep their real rates quote-only. Budgeting starts with the meter.

Content Management, Pipeline Improvements, and More

A recent update to VirtualMetric DataStream centers on how content moves into the platform and how securely it travels. Content management has been reworked around a GitOps workflow, TLS configuration has been reworked across devices and targets, and a broad set of new database devices, targets, and pipeline improvements have been added. Here’s what’s new.

How to Cut SIEM Ingest by 90% Without Losing Detection Coverage

Every SOC team knows the trade-off. Send everything to the SIEM platform and pay for it. Or filter aggressively and risk missing something. Filter lists are written once, during onboarding. Detection content keeps moving after that. Smart Engine, the new core of the VirtualMetric DataStream pipeline, takes the guesswork out of that decision. It reduces SIEM ingest using your registered detection rules. An event that no registered detection could match is dropped.

NIST Security Best Practices for Telemetry Data: How to Implement and Automate Them

NIST security best practices for telemetry data treat logs as governed records. Every record has required content, a protection requirement, and a retention period. Eight practices cover the decisions involved, from what you collect through to how you document each filter. No single standard from the National Institute of Standards and Technology covers telemetry. The requirements sit across a controls catalog, a planning guide, and a framework.

Splunk Pricing in 2026: Full Cost Breakdown (and How to Cut It)

Splunk charges you in one of two ways: by how much data you send it each day, or by how much compute your searches and dashboards use. Security teams pay for both the platform and Splunk Enterprise Security, the app that turns Splunk into a SIEM, which is priced separately on top. This guide breaks down every part of a 2026 Splunk bill, works through a real, sourced pricing example, and lays out the ways to bring the number down, including the one lever many teams overlook.

Google SecOps (Chronicle) Pricing in 2026: Full Cost Breakdown and How to Cut It

Google SecOps, formerly Chronicle, is sold in three packages priced on ingestion volume, and Google publishes no list prices for any of them. Every quote is built around your data volume, retention needs, and package tier, which makes budgeting hard without a sales conversation. This guide breaks down how the pricing model actually works, what ends up on a real bill. It also covers how to reduce that bill before data reaches the platform. Prefer to jump straight to the numbers?

Safer Pipeline Changes, Flexible Deployment, and More

August 5, 2026 The latest VirtualMetric DataStream release focuses on how pipeline changes move from idea to deployment, safely and without slowing teams down. Version 2.1 puts a deliberate step between building a pipeline and shipping it to production, along with new deployment options for Directors and multi-tenant ingestion for teams managing data across many customers. Here’s what’s new.

Microsoft Sentinel Pricing in 2026: Full Cost Breakdown (and How to Cut It)

Microsoft Sentinel’s cost is driven almost entirely by one variable: how much data you send it. That is also why so many teams underestimate their bill. A few noisy log sources or one new integration can push daily ingestion up for weeks before anyone notices. And the first signal is usually the invoice. This guide breaks down every component of a 2026 Sentinel bill.

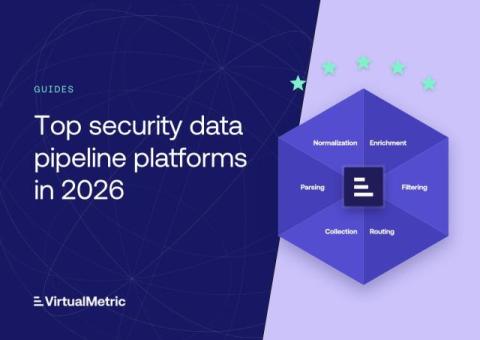
Top Security Data Pipeline Platforms in 2026: The Comprehensive Guide

The security data pipeline platform has become the most strategically important layer in the modern SOC, and in the last twelve months, the largest security vendors have paid to own it. CrowdStrike acquired Onum for $290 million, SentinelOne acquired Observo AI for $225 million, and Palo Alto Networks acquired Chronosphere for $3.35 billion. The layer that sits between your data sources and your security tools now decides what every downstream tool receives, at what cost, and in what shape.

You Can't Detect What You Never Collect: Telemetry Coverage in the Agentic SOC

Every detection rule, every threat hunt, every AI agent you deploy rests on one silent assumption: that the data describing an attack actually reached your tools. When it doesn’t, nothing above it can save you, and no one gets an alert that the data was missing. Security teams invest heavily in the sharp end of the stack: detection content, threat intelligence, response playbooks, and increasingly, AI agents to triage and investigate at machine speed.