Operations | Monitoring | ITSM | DevOps | Cloud

How much does it cost to train an AI model? Frontier figures, graded [2026]

Training an AI model costs anywhere from a few hundred dollars to several hundred million, depending entirely on what “train” means. Fine-tuning an existing model: tens to thousands of dollars. Pretraining a small model from scratch: tens of thousands to millions. A frontier run in 2026: hundreds of millions, with Epoch AI projecting the largest runs will pass $1 billion by 2027.
Shipped: See which billing connections stopped sending data, and why

Every number in CloudZero comes from a billing connection. When a credential expires or a permission changes, that connection stops sending data, and your reports show less spend than you actually have. If you catch it early, you can fix the connection before month-end close. You also need to know what broke. For Azure and Snowflake connections, CloudZero now tells you which check failed, so you can send the fix to the right person without opening a support ticket.

PHP2Shell: Manage security patches at scale with Cortex

"Patch every PHP server. Today." That was the message a lot of engineering leaders got the week of October 20. PHP2Shell is a pair of unauthenticated remote code execution bugs in PHP itself, CVE-2026-109618 and CVE-2026-109619, both rated CVSS 9.2. Attacks started before the patches shipped, and working exploits followed within days.

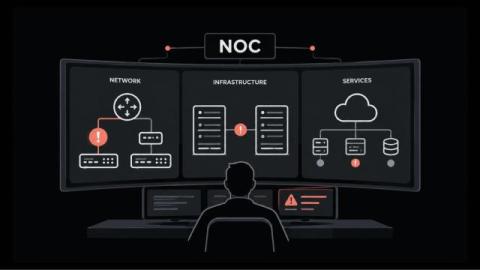
NOC Monitoring: What a Network Operations Center Tracks and How

NOC monitoring decides how fast a network problem turns into a fix. If your NOC watches the wrong layers, it misses the fault. If it alerts on everything, the real fault gets buried. According to Uptime Institute's Annual Outage Analysis 2026, 57% of operators said their most recent major outage cost more than $100,000. Most teams already collect plenty of data through network monitoring. The hard part is turning that data into a short queue of alerts that the right person acts on.

Fixing distrusted InCommon certificates with ERR_CERT_AUTHORITY_INVALID

Starting Tuesday, October 27, a lot of university websites will open in Chrome to this. Chrome is distrusting a root certificate, emSign ECC Root CA - G3, after eMudhra generated CA keys as small as 4. Every InCommon certificate issued from eMudhra’s ECC chain since April chains to that root.

7 weak points in your delivery model to fix before your next audit or outage

An auditor asking for evidence of your deployment process and an incident review asking what went wrong are asking about the same things. The difference is timing. One catches the weak point before it costs you anything. The other catches it in the middle of an outage, with a customer on the phone.

The Migration Takes 2 Weeks. Deciding to Do It Takes 6 Months. (Webinar Replay)

Replay and recap of our October 20 live session: why the decision to migrate takes longer than the migration itself, the five human blockers behind it, two customer migrations, and three ways to cut decision time. Chapters, timestamps and key takeaways. Romaric founded Qovery to make Kubernetes accessible to every engineering team. He writes about platform strategy, developer experience, and the future of cloud infrastructure.

Apache ActiveMQ CVE-2023-46604: DripDropper Exploit Explained

When a CVSS 10.0 vulnerability is published, the expectation is that affected software gets patched within days. When it involves an open-source broker that processes business-critical transactions in enterprise environments, the expectation is that the security teams responsible for those brokers treat it as an emergency. “The attacks exploit a maximum-severity security flaw in Apache.