In December 2021 we wrote VMware Monitoring: Why Opslogix is the right choice for you. At the time, vSphere 7 was new, Kubernetes was coming to vSphere, and the Log4j vulnerability was in the news. A lot has changed since then. vSphere 9 and SCOM 2025 are here, ransomware gangs now target ESXi hosts directly, and many organizations are reconsidering how they monitor their VMware estate.
IT environments change. Technologies evolve, infrastructure vendors change their strategies, and sometimes support for a monitoring integration ends. For IT teams, that can create an immediate challenge: a previously monitored part of the infrastructure suddenly becomes a monitoring gap.
How close are IT teams to total observability? See how SquaredUp uses AI to build plugins and dashboards, spot anomalies, connect data across tools, and set up monitoring from a single prompt.
Onboarding a new client shouldn't mean rebuilding the same dashboards by hand. Live demos show how our MCP server (in preview) hands that work to AI, built for MSPs, but relevant to any team automating dashboards and reporting.
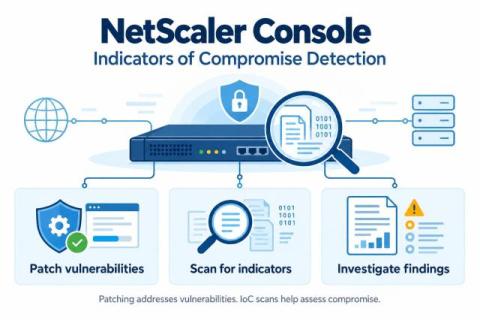
On September 27, 2026, Citrix published a security bulletin covering eight new vulnerabilities in NetScaler ADC and NetScaler Gateway. Some of these vulnerabilities are critical and have already been exploited in the wild. Citrix released fixed NetScaler builds and recommends upgrading affected appliances as soon as possible. However, when a vulnerability is already being actively exploited, installing the update only solves part of the problem.