Operations | Monitoring | ITSM | DevOps | Cloud

Starlette 1.7.0 Brings Native Tracing and Smarter Route Naming

If you’re running FastAPI, you’re running Starlette underneath it, whether you think about it or not. At Scout, we spend a lot of time thinking about what happens at that ASGI layer, since that’s exactly where our Python agent hooks in to give you request-level visibility. Starlette 1.7.0 just landed, and it’s a release worth reading closely if you care about tracing, routing, or just keeping your app running on a supported dependency chain.

Test PostgreSQL With the Queries Your App Actually Runs

The first number from my local PostgreSQL 16 test was roughly 1,600 statements per second. It looked impressive. It was also the least useful result in the run. The useful part was the workload. It came from queries the demo app had actually sent: the same prepared statements, parameters, reads and writes. A synthetic benchmark tells you how PostgreSQL handles a synthetic workload. It does not tell you whether your migration just broke the UPDATE your app depends on.

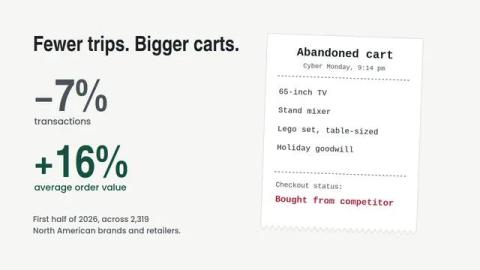
$4.48 a Gallon: Your Holiday Checkout Is the New Mall

Remember when “going shopping” meant getting in the car? This fall, filling the tank feels like applying for a small loan. U.S. regular gasoline averaged about $4.48 a gallon for the week of September 21, 2026. A round trip to the store starts competing with free shipping. And free shipping never needs a parking spot. That doesn’t tell us how many shoppers will move online this holiday season.

Free Space APIs: Useful Data for Building Smarter Applications

Space data is no longer limited to government agencies, research institutions, and specialist aerospace companies. Developers can now use APIs to bring satellite imagery, orbital information, astronomy data and other space-related datasets directly into their applications. Free space APIs are particularly useful when testing an idea or building a prototype without committing to expensive infrastructure from the outset. The right option, however, depends heavily on the type of data you actually need.

How Will Software Engineers Interface with AI in the Future? aicoding #devops #techdebate #aiagents

A breakdown of the three potential ways software engineers will interact with AI coding assistants, ranging from local desktop setups to fully automated software delivery factories. Learn more: speedscale.com.
Sponsored Post

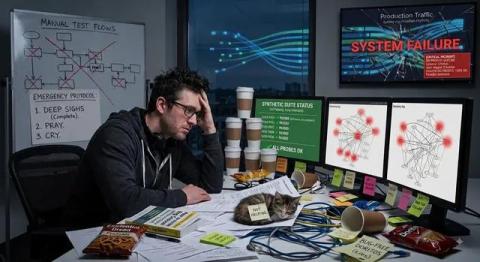
Synthetic Monitoring Is Broken. Your Production Traffic Can Fix It.

Synthetic monitoring has been a critical part of application reliability for years. It gives engineering and operations teams a way to proactively test applications, APIs, and critical customer journeys before users encounter problems. But there is a fundamental limitation with the traditional approach: Someone has to create the tests. As applications become more distributed and customer journeys become more complex, organizations can end up maintaining hundreds or even thousands of synthetic scripts. Every new feature, API, dependency, or change to a customer journey can require another update.

Upgrading the Operations Tech Stack at the Edge of Supply Chains

Warehouse management systems (WMS) and resource planning (ERP) platforms have undergone massive architectural shifts over the last decade. Microservices, event-driven cloud architectures, and real-time database synchronization have transformed how logistics organizations manage inventory levels, calculate safety stock, and track order fulfillment. Yet, despite millions invested in core IT infrastructure, operations architects frequently encounter a persistent data blind spot at the physical perimeter of the supply chain network: the loading dock.

Claude and Codex Are Slowing Your Engineering Team Down #speedscale #devops #aicoding #claude #codex

While AI coding tools dramatically slash development time, they are quietly inflating testing and maintenance burdens because teams no longer fully understand their codebase. Discover how leading engineering teams are shifting focus to testing and context packages to eliminate bottlenecks and unlock true AI efficiency.

Team-Based DLP: Give Each Group Its Own Redaction Rules

A shared Kubernetes cluster rarely belongs to one team. Payments runs checkout in one namespace, search runs search-api in another, and a risk team runs a scorer somewhere else. One Speedscale forwarder captures API traffic for all of them. Redacting that traffic before it leaves the cluster is what makes it safe to use for testing (the background is in The PII Testing Dilemma). Until now, that forwarder ran exactly one DLP rule. Every team that needed a field redacted had to edit the same JSON document.

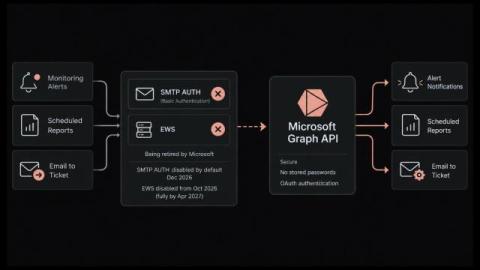
Moving Alert and Email-to-Ticket Mail off SMTP AUTH to Microsoft Graph API

Every monitoring alert, scheduled report, and email to ticket conversion in your stack depends on a mailbox. Most monitoring and helpdesk management tools still reach that mailbox the old way. They log in with a username and password over SMTP or EWS. Exchange Online is closing both doors on a published schedule. The tools that fail will fail silently. In this blog, you will: By the end, you can run the change on a weekday afternoon and know nothing went quiet.

Use AI and traffic replay to test AI-generated code

When I ask an AI agent to change code, I also want it to run the application and test what it changed. Asking it to write some tests is a start. But if it invents the expected responses from the same assumptions it used to write the code, those tests can miss the same mistake. Traffic replay gives the agent something concrete to test against: requests and responses captured from a working application.

Why Mocks Fail at Scale #softwareengineering #devops #softwaretesting #api #aicoding

Mocking for testing starts off easy, but once you scale to multiple teams and AI agents, handcrafted mocks become a serious form of technical liability. Instead of treating mocking as an individual software engineering task, shift your mindset to treat it as a platform engineering task focused on automation and continuously refreshed modern data. Watch to see how adopting technologies like traffic replay to simulate realistic backend sandboxes can transform your modern testing workflow!

eBPF: Correlating rustls Plaintext to TCP Connections Without a File Descriptor

In Under the Hood with Go TLS and eBPF, I left socket tracking as an exercise for later. The example used bpf_get_current_pid_tgid() and explicitly excluded concurrent TLS operations. Capturing plaintext was enough for that post. With rustls, later arrived: I could read the HTTP payload perfectly and still attach it to the wrong TCP connection. That’s a frustratingly convincing failure. The request looks right. The response looks right. The application works.

Are SOC 2's days numbered? #SOC2 #CodeReview #AICoding #DevOps #SoftwareDevelopment #LLM #SpeedScale

As companies adopt AI coding tools, code review processes are breaking down. Traditional compliance methods are slowing teams down, but human engineers aren't going to spend hours reading AI-generated low-level code forever. How will SOC 2 adapt to the era of AI-driven development? Drop your thoughts in the comments and subscribe for more tech insights! Learn more: speedscale.com.

Five Ways to Use OpenTelemetry Beyond Observability

OpenTelemetry graduated from the CNCF in May 2026 as, in the foundation’s own words, the de facto observability standard. The JavaScript API package alone did 1.36 billion downloads in twelve months. That kind of win has a side effect nobody plans for. Once a wire format is everywhere, has a receiver for every source, a transform language, and an agent your platform team already operates, people start putting things on it that have nothing to do with knowing whether a service is healthy.

Best API Monitoring Tools in 2026 [31 Analyzed]

The best API monitoring tools are Hyperping for HTTP and API checks with on-call and status pages, Checkly for API monitoring as code, Postman Monitors for teams that already keep collections in Postman, Datadog for connecting failed checks to traces and logs, Grafana Cloud for teams using k6, Better Stack for checks inside a broader incident workflow, and UptimeRobot for inexpensive availability checks.

From Handwritten Mocks to proxymock: The Complete Loop

Handwritten mocks are cheap one at a time. This series built enough of them to show how quickly that stops being true. Nine posts took one package notifier from a function returning "delayed" to a captured response from a real carrier. Along the way, we hand-authored canned successes, failure cases, a spy, a stateful fake, an HTTP server, response fixtures, and contract-drift tests in four languages.

How to automate sending and receiving faxes in IT processes? APIs, webhooks, integrations

It's true that fax in 2026 may seem like a technology out of place in today's DevOps environments. However, it's also true that in many regulated industries - it's still a key part of document workflows. The problem isn't necessarily the communication channel itself, but rather how it's handled. Traditional fax requires devices, phone lines, and manual document processing. API integration allows you to migrate this process to a software environment and connect it with existing systems. Curious? Let's dive in.

Did It Actually Send?

The notifier has returned a message throughout this series, which made testing almost suspiciously easy. Assert on the return value and you are done. Real notifiers do more than build strings: they send them. Once a message goes to an email provider or SMS gateway, the function may return nothing useful. When that change lands, every existing test loses the value it asserted on. This is part 4 of a ten-part series. The code is in Java, Node.js, Go and Python.

Make Failure Boring with Mocks

Every codebase has a failure path nobody has run. Not through laziness, but because reproducing it requires a backend dependency to misbehave on cue. In the package notifier, the carrier must refuse, stall, or return nonsense at the exact moment the test runs. So the retry logic ships unverified and everyone hopes. The seam from post 2 already gives the test control. A seam is a place where you can change what code does without editing that code.

Test Behavior, Not Choreography

The spy from post 4 is a sharp tool. Once a test can record every interaction, it is tempting to assert on all of them. The result looks thorough, but it is usually a transcript rather than a useful specification. This post takes a test written that way, makes a change that no customer could possibly notice, and watches the test fail anyway. This is part 5 of a ten-part series. The code is in Java, Node.js, Go and Python.

CRM API Rate Limits: What Developers Need to Know Before They Build

Every CRM integration starts the same way. You write some code, test it against a sandbox account with a few hundred contacts, and everything works beautifully. Then you push to production, where the account has 50,000 records and three other integrations pulling data at the same time, and suddenly you're drowning in 429 errors.

We Let AI Agents Rewrite a 92M-Message-a-Day Service in Go. Zero Incidents.

Our Results Daemon processes about 92 million messages a day. We recently rewrote it from Node.js to Go, and we let Claude Code write it. We wanted to know whether we could trust an agentic rewrite for a critical, high-throughput production service rather than a prototype. It shipped with zero incidents, a 70% reduction in running pods, and a lighter database load.