Operations | Monitoring | ITSM | DevOps | Cloud

Deploy Your Apps and Agents Where Your Data Lives With Aiven Runtime

Everything that makes an app or agent real happens after it works on your machine. Locally coding an app is a joy: hot reload, a seeded database, a mocked API key. Then you go to ship it, and "deploy" quietly expands into a Dockerfile that behaves in CI, somewhere to actually run the container, a database it can reach, TLS, secrets wired into the environment, and a pipeline to hold it all together. The feature took an afternoon. The plumbing takes the rest of the week.
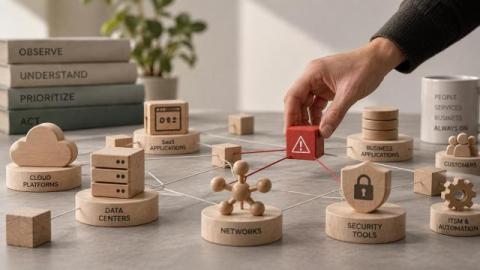
Let Builders Build, and Agents Cook.

Software used to be built by engineers. Not any more. Low-code tools brought in domain teams. AI copilots brought in everyone else. And now agents are building and acting alongside humans; marketing, finance, HR and legal are all shipping the apps they used to file tickets for. The number of people (and things) building on your data has exploded, and it isn't slowing down. And there's no single, standardized way to build, there likely never will be.

The Clearinghouse For AI Agents Has A Blind Spot

Jamin Ball’s recent piece, “Systems of Record Won the SaaS Era — Clearinghouses Will Win the Agents Era,” is the cleanest articulation I’ve seen of where the durable moat goes next. His argument is simple and, I think, correct: the SaaS era rewarded whoever owned the system of record, and the agent era will reward whoever owns the clearinghouse.

How we automated feature-flag cleanup with Agentic Pipelines

The hard part of a feature flag is rarely adding it. It is remembering to remove it months later, when the rollout is over, the original context has faded, and there is always a more urgent piece of work waiting. Since April 2026, one Atlassian team has used Agentic Pipelines to clean up their monthly backlog of stale feature flags. The workflow prepares the change and opens a pull request, while engineers still review and merge the pull request.

How Harness orchestrates LLM security scanning

Large language models are effective at security review for the same reason they are effective at many other tasks: they reason rather than pattern match. In plain terms, a traditional scanner checks code against a list of known bad patterns, the way a spell checker flags a misspelled word, regardless of what the sentence means. An LLM can instead follow the program's logic: trace a piece of attacker-controlled input through several layers of application code to determine whether it is reachable.

Your AI coding gains are stuck before the code is even written

At some point this year, you likely approved a request to expand AI coding tool access across the team. The pitch was straightforward: engineers write code faster, the team ships more, the investment pays for itself. The first half happened. Engineers are writing code faster. If you're now being asked whether the investment paid off, and you're finding the honest answer is more complicated than a yes, you are not alone, and you have not been sold something broken.

Cribl On Your Coffee Break Episode 18 - All About AI

With 3 more days to go, we’ve finally arrived at the AI episode in the Cribl on your coffee break series. Today we’ll touch on a few of the many ways we’ve enabled Cribl to use AI, and also to help you manage the data generated by AI-enabled tools. By the time the month is over, you will have a pretty good idea of what Cribl can do, and how to do it. You’ll also have consumed more caffeinated beverages than is strictly appropriate...

Vulnerability Fatigue: When Discovery Outpaces Remediation Capacity

Recent findings from Anthropic’s Project Glasswing offer a useful indication of where vulnerability discovery may be heading. Anthropic reported that it and its partners had used Claude Mythos Preview to identify more than 10,000 high- or critical-severity vulnerabilities across the software they reviewed. More significantly, Anthropic reported that the bottleneck had shifted from finding vulnerabilities to having the capacity to verify, disclose, and patch them.