Operations | Monitoring | ITSM | DevOps | Cloud



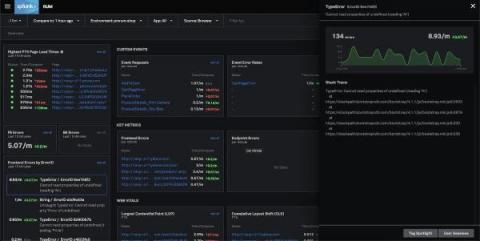
Splunk RUM Frontend Error Monitoring is Now Generally Available!
Debugging errors is an essential component to SRE and developer workflows. “How do we prioritize and isolate JavaScript errors more effectively?” is a top challenge we hear from engineering teams looking to improve end-user experience. Therefore, we are excited to announce the general availability of Splunk RUM frontend error monitoring.
Five Critical Insights You Won't Get With Your Cloud Provider's Monitoring Solution Alone
When meeting with a current or prospective Splunk customer, one question we are often asked is “Why do I need Splunk when I can just use AWS Cloudwatch, Azure Monitor, or GCP Cloud Operations Suite (formerly known as Stackdriver) for my cloud monitoring needs?” And what a great question it is!
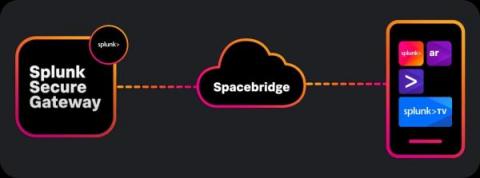
Splunk Mobile, iPad, AR and TV in Private Networks
Having Splunk Mobile available in your pocket is great, but what if you're not able to take advantage of it because of Defense Federal Acquisition Regulation Supplement (DFARS) requirements or security concerns? Through this blog post, you'll learn how deploying a Private Spacebridge might be the right answer!

Splunk AR - What's new .conf 2021
Enabling the Self Driving Cloud with Splunk Observability Cloud and GKE Autopilot
In 2021, any time that you access any kind of web service, whether it be via a website or app, chances are high that the backend is running on Kubernetes. Hundreds of thousands of organizations rely on Kubernetes to power and manage their mission critical services every day, and the reliability and scalability benefits offered by Kubernetes have been felt across the industry.
Splunk Cloud Self-Service: Announcing The New Admin Config Service API For Private Applications
In our last blog, "Splunk Cloud Self-Service: Announcing the Admin Config Service (ACS)" we introduced our modern, cloud-native API that is enabling Splunk Cloud Platform admins to manage their environments in a self-service fashion. In this blog, we take a look at our latest effort to empower our customers: ACS private app management.
Atlassian: Accelerating Observability in the Data Age
High Five: The Latest Integrations from Splunk, Microsoft and GitHub
Hello Splunk Nation! Welcome to the latest roundup of Splunk integrations with Microsoft and GitHub! Hopefully, you had a chance to virtually attend.conf21 and check out all the amazing content. For those of you who missed it, we’re recapping the Microsoft, GitHub and Splunk highlights below.

Introducing... Splunk for iPad!
Are you busy and on the go but still need to dig into your data and view your dashboards? We’ve got you covered — introducing… Splunk for iPad! Splunk for iPad is designed for and dedicated to what’s unique and great about the iPad, taking full advantage of its portable and interactive nature with unique dashboard annotation and note-taking features.