Deleting Fields with BindPlane OP
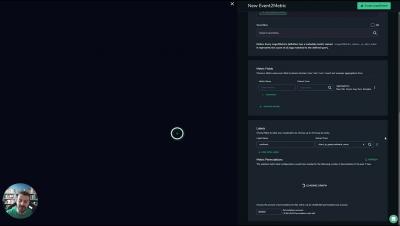
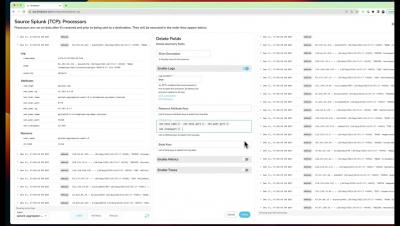
Are you ingesting unnecessary fields? See how to use the "Delete Fields" processor to remove fields from your log stream in BindPlane OP. Then use our live preview capabilities to see the changes prior to rolling out to your agents. About ObservIQ: observIQ brings clarity and control to our customer's existing observability chaos. How? Through an observability pipeline: a fast, powerful and intuitive orchestration engine built for the modern observability team. Our product is designed to help teams significantly reduce cost, simplify collection, and standardize their observability data.