Operations | Monitoring | ITSM | DevOps | Cloud

The Secure PaaS Alternative: Keep the PaaS Experience, Run It on Your Own Cloud

Railway, Northflank and seven other developer platforms disclosed breaches in October 2026. Here is why a shared PaaS turns one breach into everyone's breach, how Qovery gives you git-push deploys while your apps and data run in your own AWS, GCP, Azure or Scaleway account, and what Qovery still holds. Romaric founded Qovery to make Kubernetes accessible to every engineering team. He writes about platform strategy, developer experience, and the future of cloud infrastructure.
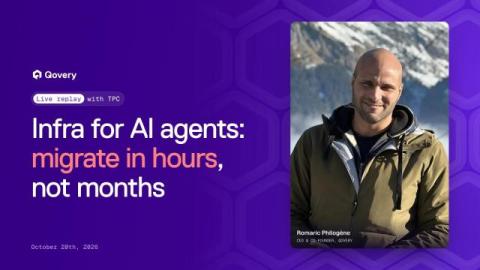
Infrastructure for AI Agents: Migrate in Hours, Not Months (Live Replay)

Replay and key takes from our October 20 live with TPC: why Day Two is 80% of infrastructure work, why shared staging breaks when agents write the code, how agents cut migrations from months to hours, and how to keep agents under control with policy tokens and audit logs. Romaric founded Qovery to make Kubernetes accessible to every engineering team. He writes about platform strategy, developer experience, and the future of cloud infrastructure.
Plug Qovery Into the Kubernetes Cluster You Already Run

BYOK on EKS, GKE and Kapsule now runs through the Qovery Operator: install it once with Helm on a cluster you already run, and deploy Qovery's component updates from the Console. Now in Preview, for clusters without cert-manager, ExternalDNS or Envoy Gateway. Pierre is a staff engineer on the Qovery platform team. He works on the Qovery Operator and the platform catalog that install and update Qovery on Kubernetes clusters.

The Migration Takes 2 Weeks. Deciding to Do It Takes 6 Months. (Webinar Replay)

Replay and recap of our October 20 live session: why the decision to migrate takes longer than the migration itself, the five human blockers behind it, two customer migrations, and three ways to cut decision time. Chapters, timestamps and key takeaways. Romaric founded Qovery to make Kubernetes accessible to every engineering team. He writes about platform strategy, developer experience, and the future of cloud infrastructure.
Strengthening the Security of Qovery's Access to Your AWS Account

Qovery now sends your organization ID as the sts:ExternalId when it assumes the IAM role in your AWS account, and the role's trust policy only accepts it on behalf of your organization. Your role is already updated. If you manage it with the qovery-role-creation CloudFormation stack, update the stack to the latest template. Romain is a staff engineer at Qovery working on the control plane and AI integrations. He writes about distributed systems, incident response, and MCP-based tooling.

Sandbox Environments for AI Agents: A Full, Isolated Stack for Every Task

A code sandbox like Daytona or E2B isolates a process. A sandbox environment isolates a whole stack: services, databases, queues and configuration, cloned for one agent task and destroyed when it is done. Here is how sandbox environments work, what they are good for, and how to run them on Qovery. Romaric founded Qovery to make Kubernetes accessible to every engineering team. He writes about platform strategy, developer experience, and the future of cloud infrastructure.
How to Stop Secrets Leaking From Your Deployment Platform, and How Qovery Stores Yours

Railway's disclosure of leaked customer environment variables is a reminder that deployment platforms hold the keys to everything. Here is how secrets leak from platforms, the practices that prevent it or limit the damage, and exactly how Qovery stores secrets across its control plane and your data plane, with AWS Secrets Manager, Parameter Store, GCP Secret Manager, Doppler and Infisical. Romaric founded Qovery to make Kubernetes accessible to every engineering team.

Where to Find GPU Capacity in 2026: Hyperscalers, Neoclouds and Regional Clouds

Google, CoreWeave and Nebius all say they are short of GPUs. Here is where capacity still exists in 2026, which GPU clouds offer managed Kubernetes, how to connect a second cloud to your first one, and how to run GPU services on all of them from one platform. Romaric founded Qovery to make Kubernetes accessible to every engineering team. He writes about platform strategy, developer experience, and the future of cloud infrastructure.
GCP Out of Capacity? How to Offload Workloads to AWS Without Running a Second Platform

Google says it is compute constrained, and GKE teams now hit ZONE_RESOURCE_POOL_EXHAUSTED on CPU machine families, not only GPUs. Here is what the error means, what Google recommends, what AWS can and cannot offer, and how to offload workloads from GCP to AWS with one platform instead of two. Romaric founded Qovery to make Kubernetes accessible to every engineering team. He writes about platform strategy, developer experience, and the future of cloud infrastructure.
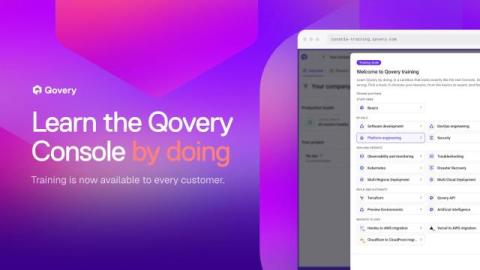
Introducing Qovery Training: Learn the Console by Doing, Before You Touch Production

Qovery Training is now generally available to every Qovery customer. It is a sandbox copy of the Console on fake data, with 18 tracks for software engineers, DevOps, platform and security teams, a simulated terminal and AI agent, and training spaces where admins pick the lessons and follow their team's progress. Romaric founded Qovery to make Kubernetes accessible to every engineering team. He writes about platform strategy, developer experience, and the future of cloud infrastructure.