Operations | Monitoring | ITSM | DevOps | Cloud

Unfolding the Twitter security incident

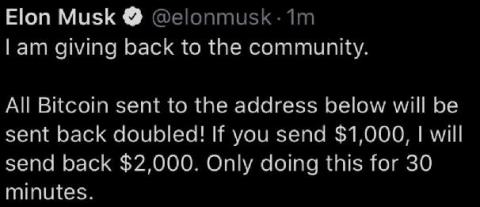
In case 2020 wasn’t dystopian enough, here’s some more unbelievable news. On July 15, 2020, social media giant Twitter admitted it fell victim to a security breach. The attackers targetted 130 Twitter accounts, including several belonging to high-profile individuals such as elected officials; former president Barack Obama; and business leaders including Bill Gates, Jeff Bezos, and Elon Musk.
Australia's Department of Health Suffers PHI Breach Due to Pagers

In an unprecedented incident that has left medical authorities in Western Australia (WA) in disbelief, a local teenager has been found to be the mastermind behind a massive data breach. The breach intercepted thousands of names, phone numbers and communications between doctors responding to the COVID-19 crisis from their pagers. This is an unfortunate incident and a simple reminder of how pagers jeopardize the security of sensitive patient information.

Protect your Elasticsearch deployments against attacks like "meow bot" - for free

The issue of unsecured databases is growing. In 2019, 17 percent of all data breaches were caused by human error — twice as many as just a year before. And the IBM/Ponemon 2019 report found that the estimated probability of a company having repeated data breaches within two years grew by 31 percent between 2014 and 2019. Why is this happening?

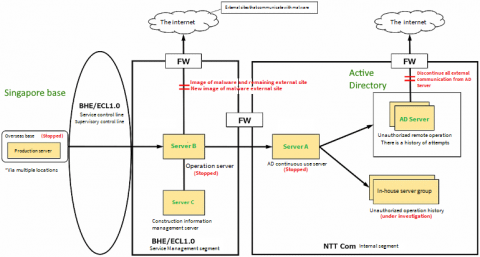
Telecommunications giant reveals an Active Directory server breach. What can we learn from it?

We’ve always been vocal about the imminent threat of breaches and propagated the message that irrespective of the size of your business, the industry you’re in, or your geography, you can be subject to a security breach. And unfortunately, history repeats itself often. On May 11, 2020, Nippon Telegraph & Telephone (NTT), a large telecommunications company, revealed that attackers may have stolen data from its internal systems, affecting over 600 customers.

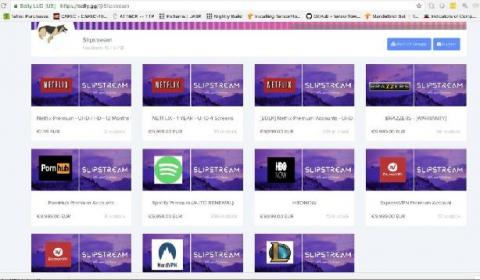
The value of a stolen account. A look at credential stuffing attacks.

A type of credential reuse attack known as credential stuffing has been recently observed in higher numbers towards industry verticals. Credential stuffing is the process of automated probing of and access to online services using credentials usually coming from data breaches, or bought in the criminal underground.

Kubernetes Security: Lateral Movement Detection and Defense

What is Lateral Movement? Lateral movement refers to the techniques that a cyber-attacker uses, after gaining initial access, to move deeper into a network in search of sensitive data and other high-value assets. Lateral movement techniques are widely used in sophisticated cyber-attacks such as advanced persistent threats (APTs).

Improving Cybersecurity Starts at the Endpoints

Careful monitoring and attention to endpoints are just two elements of a strong cybersecurity strategy for K-12 districts. Cybersecurity must be a top priority for K-12 schools. Schools need to prioritize thwarting industrious hackers who are intent on getting to the treasure trove of information and personally identifiable information (PII) schools manage.

Email, security, and breaches

Email-based attacks can take many forms, and are typically deployed by cybercriminals in order to extort ransom or leak sensitive data. Just recently, a banking Trojan named Trickbot targeted Italy, a hotspot for COVID-19 cases, with email spam campaigns. While the email subject line is in line with the daily concerns and talks about spread of the virus, the attachment was actually a malicious script.

Apple in 2018, now Tesla-who's next in the line of internal data leaks?

Recent allegations of an ex-Tesla employee syncing the Autopilot source code to his personal iCloud account is yet another classic case of how poor data security is, even in some of the most technologically advanced organizations. The Tesla leak isn’t even the first time that a data breach of such immense magnitude pertaining to self-driving technologies has occurred; in July 2018, an Apple employee was caught using AirDrop to transfer 40GB of confidential data to a personal PC.