Operations | Monitoring | ITSM | DevOps | Cloud

Announcing HAProxy Enterprise 3.2

HAProxy Enterprise 3.2 is a pivotal release that reinforces the product’s identity as both the world’s fastest software load balancer and a sophisticated edge security layer. This release brings next-generation security intelligence, extends its industry-leading performance, and expands the native routing and integration capabilities in HAProxy Enterprise.
Black Hat USA 2025 recap

They say what happens in Vegas stays in Vegas—but this year, we couldn’t keep the latest in cybersecurity to ourselves. Though it wasn’t our first time attending Black Hat USA (we’re no strangers to the neon lights and desert heat), our anticipation was high when we landed at LAS. We couldn’t wait to get to the show, connect with security professionals, learn more about where the industry is headed, and put our own solutions to the test.

HAProxy Enterprise WAF protects against Microsoft SharePoint CVE-2025-53770 / CVE-2025-53771

Critical vulnerabilities in Microsoft SharePoint (CVE-2025-53770 and CVE-2025-53771) are currently being exploited in the wild. Disclosed on July 19, 2025, these vulnerabilities have CVSS scores of 9.8 and 7.1 respectively, indicating severe and high risk. CVE-2025-53770 affects on-premises Microsoft SharePoint Servers, allowing unauthorized attackers to execute code over a network. CVE-2025-53771 affects Microsoft Office SharePoint, allowing authorized attackers to perform spoofing over a network.

HAProxyConf 2025 Recap

A lot can change in three years. The world of 2022 was a quite different place. Queen Elizabeth II was the longest-serving living monarch, the world population hadn’t yet cracked eight billion, and many of us were still emerging from the strangeness of the Covid years. Meanwhile, at HAProxyConf 2022, we unveiled HAProxy Fusion Control Plane for the first time.

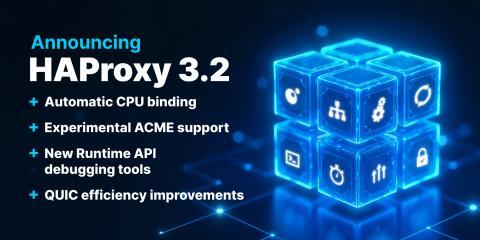
Announcing HAProxy 3.2

HAProxy 3.2 is here, and this release gives you more of what matters most: exceptional performance and efficiency, best-in-class SSL/TLS, deep observability, and flexible control over your traffic. These powerful capabilities help HAProxy remain the G2 category leader in API management, container networking, DDoS protection, web application firewall (WAF), and load balancing.

Protecting Against SAP NetWeaver Vulnerability (CVE-2025-31324) with HAProxy

A critical vulnerability in SAP NetWeaver (CVE-2025-31324) is currently being exploited in the wild. Disclosed on April 24, 2025, this vulnerability has the highest possible CVSS score of 10.0, indicating severe risk. The vulnerability affects SAP NetWeaver Application Server Java's Visual Composer Framework (version 7.50), allowing unauthenticated attackers to upload arbitrary files to NetWeaver servers. This can lead to remote code execution and complete system compromise.

The State of SSL Stacks

A paper on this topic was prepared for internal use within HAProxy last year, and this version is now being shared publicly. Given the critical role of SSL in securing internet communication and the challenges presented by evolving SSL technologies, reverse proxies like HAProxy must continuously adapt their SSL strategies to maintain performance and compatibility, ensuring a secure and efficient experience for users. We are committed to providing ongoing updates on these developments.