Operations | Monitoring | ITSM | DevOps | Cloud

Microsoft Offers 60,000 Employees Buyouts. Here's the AI Problem.

Microsoft is offering voluntary buyouts to 60,000 employees—more than a quarter of its workforce—while investing billions into AI infrastructure. But here's the bigger question: What happens when experienced engineers leave and AI-generated code keeps accelerating? AI can write code faster than ever. But deploying it safely, securely, and at scale? That's becoming the real bottleneck. Is Microsoft funding AI with headcount instead of efficiency?
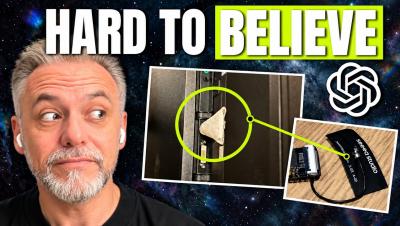
Was Saudi Arabia Secretly Listening to OpenAI's Biggest Secrets?

A hidden recording device. A former OpenAI engineer. And a possible connection to the Saudi government. What started as a suspicious discovery behind a television inside OpenAI has turned into a federal investigation with potential national security implications. The FBI is investigating whether former OpenAI engineer Abdulrahman Alfozan was involved in corporate espionage, with prosecutors pointing to alleged connections to a member of the Saudi royal family.

Microsoft Has a Bigger Problem Than Anyone Realizes

Microsoft just released over 1,400 security patches, including three zero-day vulnerabilities, one of which is already being exploited. But is this a sign of better security or a much bigger problem? In this ShipTalk discussion, we break down Microsoft's massive Patch Tuesday release, the challenges of managing thousands of vulnerabilities across enterprise environments, and whether AI is helping Microsoft find problems too late in the software development process.

AI Can Write Infinite Code. But Can We Ship It Safely?

AI is making code generation faster than ever. But writing code is only half the battle. Neil Watkins from Burns & McDonnell explains why the next big challenge in AI-driven software development isn't generating more code. It's making sure that code can be tested, secured, and deployed safely. As AI accelerates development, businesses need to rethink how they manage risk and ship software with confidence.

Security Just Hit Machine Speed

What if we could eliminate vulnerabilities before they become a problem? Neil Watkins from Burns & McDonnell explains how AI, automated security assessments, and Harness CI/CD capabilities could transform vulnerability management. From reducing attack surfaces to rapidly responding to critical zero-day vulnerabilities, the future of security is about moving faster without slowing down developers.

php2shell: the flaw hiding all across the web

Discover how php2shell vulnerabilities expose PHP servers to remote code execution and how Harness virtual patching protects endpoints while you deploy fixes. On October 21, 2026, the PHP project rushed out emergency patches for two critical flaws nicknamed php2shell (CVE-2026-109618 and CVE-2026-109619, both rated 9.2 out of 10). This isn't a bug in some plugin or a server someone set up wrong. It's in PHP itself, in the way the language has handled errors since 2012.

Bring Your Own Identity Provider to Harness MCP

Learn how Harness MCP OAuth proxy mode enables enterprise developers to use their own identity provider without static tokens or shared credentials. OAuth proxy mode lets enterprises run Harness MCP behind their own identity provider, with no static tokens anywhere in the chain. Coding agents write the change. Harness agents take it through production, running the builds, tests, scans, and deployments that follow, with policy enforced on every action.